

Discover TÜV-certified GoogleTest with Agentic AI for C/C++ testing!
Get the Details »
Jump to Section
Parasoft Blog


Embedded systems have been with us for ages. Read on to learn what they are, some safety concerns of embedded systems, and how proper testing can help make them safe and secure.
Jump to Section
Embedded systems are the dedicated computing engines behind modern products and infrastructure, enabling devices to sense, process, and act on the physical world with speed and reliability.
Embedded systems are specialized computing systems designed to perform dedicated functions within a larger product or system. They’re the hidden intelligence behind many of the technologies we depend on every day, from automobiles, aircraft, medical devices, and industrial robots to smart appliances, telecommunications equipment, and connected infrastructure. Since they’re often security- or safety-critical, automated testing for embedded systems is essential.
Unlike general-purpose computers, embedded systems combine hardware and software for a specific purpose. They usually operate under strict constraints for processing power, memory, energy consumption, timing, reliability, safety, and cost.
But embedded systems are changing. Today’s embedded systems are increasingly connected, software-defined, and intelligent. Artificial intelligence (AI) and machine learning (ML) are moving computation from traditional data centers to embedded and edge devices, while AI-assisted development is changing how engineers create, test, and verify the software running on them.
Embedded systems power devices across nearly every industry. They’re not optional enhancements. They’re the operational core of modern technology. Here are a few examples.
Embedded systems provide the intelligence inside smartphones, smart TVs, wearables, appliances, and smart home devices. They manage functions such as power consumption, wireless communication, sensor processing, displays, and user interaction.
Increasingly, these devices also execute AI workloads locally. Voice recognition, image processing, anomaly detection, and other AI capabilities can run directly on embedded or edge processors rather than depending entirely on cloud infrastructure.
Modern vehicles contain extensive networks of electronic control units (ECUs) and increasingly powerful centralized or zonal computing architectures. Embedded software controls braking, steering, battery management, powertrain functions, airbags, advanced driver assistance systems (ADAS), connectivity, and many other vehicle functions.
As vehicles become more software-defined and AI-enabled, embedded computing also supports perception, decision support, driver monitoring, and increasingly sophisticated automated driving capabilities.
These systems must operate reliably and often in real time under demanding environmental and safety conditions.
Pacemakers, infusion pumps, patient monitors, imaging equipment, surgical systems, and other medical devices depend on embedded software that must be precise and reliable.
AI is also expanding the capabilities of medical technology through applications such as medical image analysis, patient monitoring, anomaly detection, and decision support. As intelligence moves closer to the patient and device, the reliability of both AI-enabled functionality and the conventional software surrounding it becomes increasingly important.
Embedded systems run factory automation, robotics, railway signaling, avionics, power infrastructure, and industrial control systems.
Modern robots are a particularly good example of how embedded computing is evolving. Sensors, real-time control software, AI perception models, motion planning, networking, and safety mechanisms may all operate together within the same system. The result is a combination of traditional deterministic embedded software and increasingly complex AI-driven behavior.
What separates an embedded system from a general-purpose computer? Primarily, its purpose and operating constraints.
Embedded systems are designed to perform specific functions. Unlike a desktop computer that can run thousands of unrelated applications, an embedded controller is engineered around the behavior required by the product.
For example, a braking controller must continuously monitor inputs, execute control logic, detect faults, and activate braking components within defined timing constraints.
Embedded systems often operate with limited processing power, memory, storage, power, and thermal capacity. Engineers must balance software functionality with the capabilities and cost of the underlying hardware.
These constraints are becoming especially important as AI workloads move onto embedded processors, GPUs, neural processing units (NPUs), and other specialized accelerators.
Many embedded systems are real-time systems, meaning that they must respond to events within specified deadlines.
In safety-critical environments such as automotive braking, medical devices, industrial control, or avionics, producing the correct result too late may still constitute a system failure. Correctness therefore depends on both what the system does and when it does it.
Embedded products may operate continuously for years or even decades. They must behave predictably, tolerate faults, and remain stable under environmental and operational stresses.
At the same time, connectivity and software-defined architectures are making post-deployment updates increasingly common. Embedded software engineering must therefore address not only initial release quality but also how systems are maintained, updated, verified, and secured throughout their operational lives.
Embedded software interacts directly with sensors, actuators, motors, communication interfaces, memory, processors, and specialized accelerators. Hardware and software are therefore often designed and optimized together.
This tight relationship with the physical world is one of the fundamental differences between embedded and traditional enterprise software.
Embedded system architectures vary considerably depending on complexity, performance, safety, security, and real-time requirements. The use of a microcontroller architecture is unique to embedded systems.
A simple embedded microcontroller may contain a CPU, RAM, ROM or flash memory, input/output interfaces, sensors, actuators, communication interfaces, and a human-machine interface.
More advanced systems may incorporate multicore processors, GPUs, NPUs, high-speed networking, virtualization, multiple operating systems, and AI/ML models.
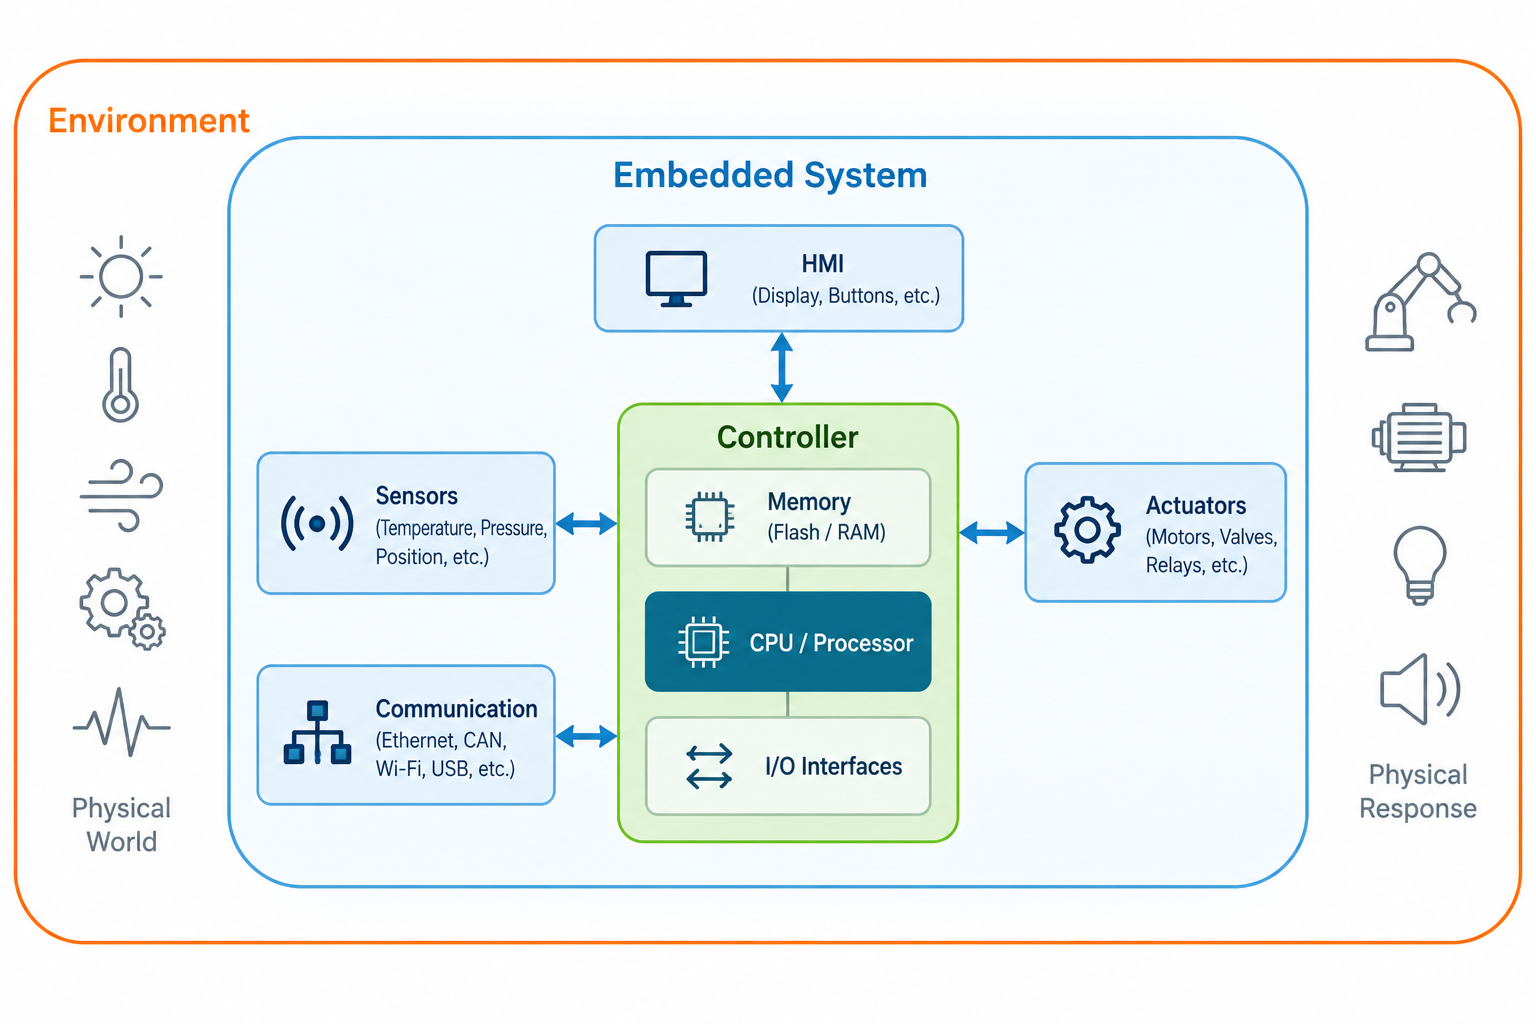
A typical embedded system connects sensors, actuators, communication interfaces, and a human-machine interface (HMI) to a controller that processes inputs and interacts with the physical environment.
At the simplest level, an embedded application may execute continuously within a loop. The software reads inputs, processes information, updates outputs, and repeats.
A related architecture is the control loop, where the system repeatedly measures a physical state, such as temperature, speed, pressure, or position, compares it with a target value, and adjusts an actuator accordingly.
These architectures provide advantages such as determinism, low resource consumption, and straightforward implementation. However, they become harder to scale as concurrency, communications, and functionality increase.
Interrupt-driven systems allow hardware events to trigger software routines immediately rather than waiting for the main application loop.
Multitasking architectures extend this approach by allowing multiple software tasks to share processor resources using techniques such as priority-based scheduling, time slicing, or cooperative task switching.
These architectures are widely used when systems must simultaneously handle sensor processing, communications, user interaction, control functions, and fault management.
More sophisticated embedded systems often use a real-time operating system (RTOS) to provide scheduling, intertask communication, timing services, memory management, and hardware abstraction.
Layered architectures further separate hardware drivers, system services, middleware, and application functionality. This improves modularity, portability, testability, and maintainability.
Modern safety-critical systems may go further still, using multicore processors, partitioning, virtualization, heterogeneous computing, and specialized AI accelerators to consolidate increasingly sophisticated software onto powerful computing platforms.
Embedded hardware is selected to meet both technical and business requirements. Because products may be manufactured in the millions, even small differences in processor, memory, power, or component costs can have a significant economic impact.
Typical constraints include:
These constraints become more challenging as embedded software grows more sophisticated. AI workloads, advanced sensor processing, connectivity, cybersecurity, and software-defined functionality can dramatically increase computing requirements.
As a result, modern embedded systems range from small microcontrollers to multicore 64-bit processors and heterogeneous systems that combine CPUs, GPUs, and dedicated AI accelerators.
Software has become one of the primary sources of differentiation and innovation in embedded products.
Embedded software can range from a few thousand lines of code running on a bare-metal microcontroller to millions of lines distributed across processors, operating systems, middleware, applications, open source components, and AI models.
Small embedded applications typically run on microcontrollers without a formal operating system. They may control a single subsystem using a limited number of sensors and actuators.
Their simplicity makes them resource-efficient and highly deterministic.
More complex applications often use commercial or open source RTOSs or embedded Linux. These environments provide services for multiprocessing, multithreading, networking, hardware abstraction, and communications.
Applications can range from industrial controllers and connected devices to safety-critical systems in transportation and medical technology.
Large embedded systems increasingly resemble sophisticated distributed computing environments. They may contain multicore processors, virtualization, high-performance networking, large software stacks, and multiple applications running simultaneously.
Software-defined vehicles, autonomous machines, telecommunications infrastructure, advanced robotics, and aerospace systems demonstrate how far embedded computing has evolved from the traditional microcontroller.
One of the biggest changes in embedded engineering is the growing role of AI. There are two dimensions to this transformation.
This creates enormous productivity opportunities, but also a verification challenge.
AI-generated code still has to satisfy the same requirements for safety, security, reliability, coding standards, and functional correctness as human-written code. In regulated applications, developers must also be able to produce objective evidence demonstrating that the resulting software has been adequately verified.
AI can accelerate development. Verification must keep pace.
Embedded systems frequently interact with the physical world. As a result, failures can have consequences that reach far beyond a software crash.
A defect in a braking controller, medical device, industrial robot, railway system, or flight control system can result in injury, loss of life, property damage, or significant economic consequences.
Cybersecurity creates another dimension of risk.
Connected embedded devices expose communication interfaces, software components, update mechanisms, and supply chains that attackers can potentially exploit.
Because of this, teams must consider safety and security throughout the embedded software lifecycle.
Depending on the industry and application, organizations may need to comply with standards such as:
Additionally, organizations developing AI-enabled safety-critical systems may need to consider emerging AI safety standards and guidance alongside their established functional safety processes.
Safety and security cannot be added at the end of development. They require systematic verification and validation throughout the software lifecycle.
Verification activities commonly include:
Automating these activities helps engineering teams identify defects earlier, continuously assess software quality, and generate the evidence required for reviews, audits, and certification.
Parasoft helps teams automate embedded software testing and verification across development, CI/CD, and compliance workflows.
Parasoft C/C++test combines static analysis, unit testing, structural code coverage, requirements traceability, and compliance reporting to help teams develop safer, more secure, and more reliable C and C++ software.
Parasoft C/C++test CT extends continuous testing into modern CI/CD workflows and works with existing unit testing frameworks such as GoogleTest while providing structural coverage, requirements traceability, and compliance evidence.
Parasoft DTP aggregates software quality and testing information to provide centralized analytics, dashboards, trend analysis, and compliance reporting.
Together, these capabilities help engineering teams establish a continuous verification workflow from the developer IDE through CI/CD and target testing.
Bringing AI Into Embedded Software Verification
Parasoft is also applying AI to the verification process itself.
Through MCP-enabled AI workflows and specialized AI skills, Parasoft enables AI agents to work with structured verification information generated by C/C++test and C/C++test CT. Instead of relying solely on a generic AI model’s knowledge, agents can use information about static analysis violations, coding rules, test results, and structural code coverage to assist engineers with specific verification tasks.
AI-assisted workflows can help teams:
Parasoft DTP also uses machine learning to help prioritize static analysis findings so developers can focus attention on the violations most likely to matter.
The goal isn’t to replace engineering judgment. It’s to use AI to reduce repetitive work and help engineers move faster while maintaining the verification rigor, traceability, and evidence expected in safety- and security-critical software development.
This becomes especially important as AI-generated code becomes more common. Whether code is written by an engineer or generated with AI assistance, it still needs to be analyzed, tested, measured, reviewed, and verified before teams can trust it in an embedded system.
Embedded systems are no longer simply small computers hidden inside products.
They’re becoming connected, software-defined, AI-enabled computing systems that increasingly determine how products behave, evolve, and interact with the physical world.
At the same time, AI is changing how engineers build those systems. Code can be generated faster, tests can be created more intelligently, and AI agents can assist with verification tasks that once required extensive manual effort.
But faster development doesn’t reduce the need for engineering rigor—it makes continuous verification even more important.
As embedded systems become more intelligent and autonomous, organizations need development practices that combine innovation with systematic verification. Automated testing, continuous compliance, requirements traceability, and AI-assisted verification provide the foundation engineering teams need to deliver embedded software that remains safe, secure, reliable, and trustworthy.
Static Code Analysis for Embedded Development


